Designing a governance regime · Standard gear
Reviewed and published, version 1.0.0.
The law here is as it stood on 18 November 2026. Big Widget Company, its people and its hiring assistant are made up. Every real law, standard, paper and inquiry below is real and cited. Where this module has not checked something, it says "not checked" and names who checks it next. Nothing here is legal advice.
What this module does
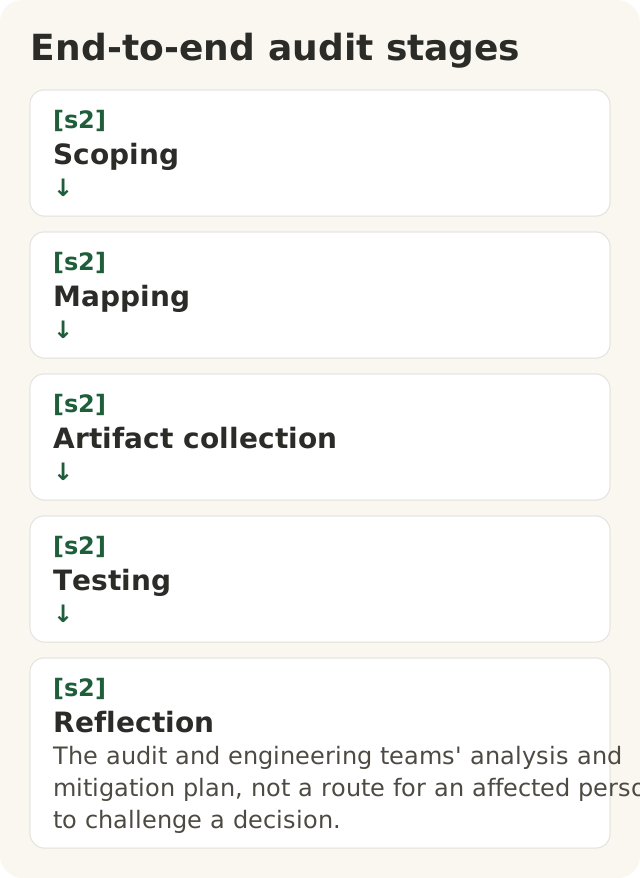
Figure data as text
End-to-end audit stages
Five stages in order. [s2]
- Scoping. [s2]
- Mapping. [s2]
- Artifact collection. [s2]
- Testing. [s2]
- Reflection: the audit and engineering teams’ analysis and mitigation plan, not a route for an affected person to challenge a decision. [s2]
Objective: 500.8-a. Text equivalent of figures/end-to-end-audit-stages.svg.
Earlier levels gave you one rule for one AI action. This module asks for the whole regime: the standing arrangement that decides, for every consequential action an AI system takes part in, who decides, what gate it passes first, what evidence is kept, and how a person can challenge the result and get it put right.
By the end you will be able to:
- design a governance regime for Big Widget Company that names the decider, the gate before each consequential action, the evidence kept and the route to challenge and remedy (500.8-a);
- for a dated hiring-assistant scenario, test the role procurement has assigned, name the missing role, classification and transition facts, and build a clause → gate → evidence → owner table from the original and amending legal text, keeping voluntary guidance and an ISO catalogue entry in their place (500.8-b);
- explain, using two documented public-sector failures, why contestability and an end-to-end audit trail have to be designed in, not added after harm (500.8-c).
The module builds on 300.7, where you learned the Act's risk structure and the provider and deployer capacities. Here you apply both to a regime you could defend.
A regime is decisions, not a document
The misconception
A common belief is that an organisation "has AI governance" once it adopts a framework document. A framework can help, but it does not decide anything. People do.
This course asks four questions of any regime. The four questions are the course's own design. No framework cited below sets them out this way.
| Element | The question | A regime fails here when… |
|---|---|---|
| Decider | Which named role says yes or no, can stop the action, and actually makes the call? | "The business" decides, so no one does; or the system acts before the named person has decided. |
| Gate | What must be true, and checked, before this consequential action runs? | The check happens after the action, or the system checks itself. |
| Evidence | What record is kept, by whom, for how long, so someone else can reconstruct the decision? | Logs exist but no one can link an outcome to the input, rule and person behind it. |
| Remedy | How does an affected person challenge the result, who reviews it, and what can they change? | The only route is a general complaints inbox with no power to reverse anything. |
Remove any one and the regime breaks in a specific way. No decider: a gate with no one who can release or refuse it. No gate: a decider who hears about the action after it happened. No evidence: a remedy that cannot find what went wrong. No remedy: harm that is recorded perfectly and never put right.
A named decider on paper is not enough. Test whether that person actually makes each decision. If the tool sends a rejection on its own, the decider test fails as well as the gate test.
What the guidance says, and what it is
NIST's AI Risk Management Framework is voluntary guidance from a US standards agency, not law.1 It does not use this course's four questions, but several of its outcomes overlap with them. It asks that roles and responsibilities for managing AI risks "are documented and are clear to individuals and teams throughout the organization", and that the risk management process and its outcomes "are established through transparent policies, procedures, and other controls".1 It asks for policies to collect and integrate feedback from people outside the team that built or deployed the system about its impacts, and for post-deployment monitoring plans that include mechanisms for appeal and override.1
NIST's companion Playbook "includes suggested actions, references, and related guidance", and NIST says the framework and the Playbook "are intended for voluntary use". Organisations may borrow "as many – or as few – suggestions as apply".2 So the Playbook is a source of ideas. One further point is this course's, not the Playbook's: following its suggestions is not, by itself, evidence that any legal duty is met.
Raji and colleagues proposed a framework for internal algorithmic auditing meant to run "end-to-end", throughout the development lifecycle rather than once at the end.3 Its stages (scoping, mapping, artifact collection, testing and reflection) each produce documents, and together those documents form the audit report.3 That is the evidence element, built as the work goes, not reconstructed later. Their reflection stage is the audit and engineering teams' analysis and mitigation plan, not a route for an affected person to challenge a decision.3 The remedy element is this course's addition.
People decide; the assistant does not
The Foundation's manifesto states the rule plainly: "No direct model-to-tool path for consequential actions."4 Rejecting an applicant is consequential. So in this regime the assistant ranks, and a named person decides. The manifesto also gives a gate four possible answers: "go ahead · only this far · wait for a person · no".4 This course's shorthand for them is allow, constrain, hold, deny. Every gate below gives one of those answers, and the regime names the person who can release each hold. "Human in the loop" is not enough on its own; the regime says which human, for which action.
Big Widget Company's hiring regime
The scenario, dated 18 November 2026: Big Widget Company's EU subsidiary uses a purchased hiring assistant, under its own authority, to rank EU job applicants for review by HR. Procurement has labelled the company a "deployer". The HR governance lead owns the gates before ranking use, before any rejection and before a challenge is resolved. The packet does not say who developed or commissioned the system, who placed it on the market or put it into service, under whose name, or when; whether Big Widget has put its own name on it; or whether Big Widget's configuration changed its intended purpose or substantially modified it.
Here is a regime for that system. The deciders and gates follow the scenario. The evidence and remedy columns, and the rules pack, are this course's design, not a legal requirement.
| Consequential action | Decider | Gate (checked before the action) | Evidence kept | Challenge and remedy |
|---|---|---|---|---|
| Configure or change the assistant | HR governance lead, with legal counsel | Role, classification and transition memos updated (see 500.8-b); no change to intended purpose or design without a new review | Change log: what changed, who approved, which memo version; new rules-pack version | Any named overseer can halt a change pending the memo |
| Start ranking applicants | HR governance lead | Memos signed; oversight staff named and trained; applicants told that an AI system is used; rules pack lodged for independent review; stop procedure tested | Go-live record; named overseers; notice text and version; rules-pack version | Applicants are told how to ask for human review and for an explanation |
| Reject an applicant | HR reviewer named in the go-live record. The assistant has no path to send a rejection | A person reviewed the application itself, not only the rank, and recorded a reason | Decision record linking applicant reference, where the application is kept, model version, rules-pack version, rank, reviewer, reason, time | Rejection notice says how to challenge, how to ask for an explanation, and by when |
| Resolve a challenge | HR governance lead, with a reviewer who did not make the original decision | The decision record and the rules pack in force have been retrieved and re-examined; the reviewer can reverse | Challenge record: grounds, what was re-examined, outcome, what changed | Reversal reinstates the applicant; repeated grounds reopen the "start ranking" gate |
| Stop the assistant | HR governance lead; any named overseer may pause | None, by design: stopping is always allowed, and the regime says so in writing | Stop record and reason | Restart only through the "start ranking" gate again |
Three design points.
- The remedy depends on the evidence. A reviewer cannot re-examine a rejection that left no record linking the outcome to its inputs and the rules in force.
- The challenge reviewer is not the person who decided. That separation is this course's choice, in the same spirit as Raji and colleagues' case for audit inside the development process.3
- A decision record is not a receipt. The decision record holds applicant details, so it is a controlled work record: access is limited, and how long it is kept follows the log rule and data-protection law. If Big Widget issues a signed receipt for a gate decision, the Foundation's rule applies. A receipt carries "hashes, decision, tier, policy hash, key id" and never "prompts, outputs, payloads, personal data".5 No applicant's name, application or rank goes in a receipt.
The three yeses for the hiring assistant
The manifesto ties three movements, Get to Yes, Stay at Yes and Recover to Yes, to moments in a system's life.4 Here is what each looks like for Big Widget.
- Get to Yes, "before a rule or a system ships" and "before a single action runs".4 This is the "start ranking" gate. The yes is conditional: this tool, this purpose, these settings, this rules-pack version. If the transition memo (Step 4 below) is still open, the answer is "wait for a person", and the person is legal counsel.
- Stay at Yes, "while it runs, in real time".4 Named overseers watch the ranking. The HR governance lead reads the challenge records each month. The manifesto's checklist line applies: "I know my system's coverage number, or I know that I do not."4 Here the number is how many rejections passed through the "reject" gate, out of how many were sent. A hold nobody answers is not a yes.
- Recover to Yes, "after — on demand, on incident".4 Triggers include a challenge upheld on grounds seen before, a rejection with no decision record, or a configuration change that skipped review. The HR governance lead stops the assistant, inspects the records and fixes the cause. A stopped tool or a promised fix is not a return to yes. Big Widget is back at yes only when the "start ranking" gate passes again and the named people record that it did.
At no step does the assistant decide. It ranks under rules people wrote; people release holds, make each rejection and decide when recovery is real.
From law to gates: the hiring-assistant table
Step 1: test procurement's label
Procurement says "deployer". Under Article 3(3) of the AI Act, a provider is a person or body "that develops an AI system … or that has an AI system … developed and places it on the market or puts the AI system into service under its own name or trademark, whether for payment or free of charge".6 Both halves matter: developing (or having it developed) and placing it on the market or putting it into service under its own name. A deployer is a person or body using an AI system under its authority, except in a personal non-professional activity.6 Using the assistant under its own authority fits the deployer definition on the stated facts.6
Buying a system does not settle that the buyer is only a deployer. Article 25(1) of the original text says a "deployer or other third-party shall be considered to be a provider of a high-risk AI system", with the provider's obligations, in three cases.6 Each case is about a system that is already on the market or in service:
- (a) "they put their name or trademark on a high-risk AI system already placed on the market or put into service, without prejudice to contractual arrangements stipulating that the obligations are otherwise allocated";6
- (b) they make a substantial modification to such a high-risk system "in such a way that it remains a high-risk AI system pursuant to Article 6";6
- (c) they modify the intended purpose of a system "which has not been classified as high-risk" so that it "becomes a high-risk AI system in accordance with Article 6".6
Point (a) is about an act: a party putting its name or trademark on the system. Seeing Big Widget's logo on a screen is a fact to explain, not an answer. Who put it there, when, and under what contract? As you saw in 300.7, a company can hold both capacities at once. Whether the 2026 amendment changed any part of Article 25 is not checked here; counsel checks a consolidated text before relying on it.
So the honest finding is: deployer, supported on the stated facts; additional provider capacity unresolved. The missing role facts are:
- Who developed the system, and did Big Widget have it developed?
- Who placed it on the market or put it into service, under whose name or trademark, and when?
- Did Big Widget put its own name or trademark on it afterwards? If Big Widget's name appears, who put it there, and what does the contract say about who carries the provider's obligations?
- Did Big Widget's configuration substantially modify it, or change its intended purpose? Was it classified as high-risk before that change, and is it after?
Write these as open questions in the role memo. Do not answer them by assumption in either direction.
Step 2: classification is its own question
Annex III lists, under employment, AI systems "intended to be used for the recruitment or selection of natural persons, in particular to place targeted job advertisements, to analyse and filter job applications, and to evaluate candidates".6 Article 6(2) says systems referred to in Annex III are considered high-risk.6 Article 6(3) then sets out a derogation. An Annex III system "shall not be considered to be high-risk where it does not pose a significant risk of harm to the health, safety or fundamental rights of natural persons, including by not materially influencing the outcome of decision making".6 But such a system "shall always be considered to be high-risk where the AI system performs profiling of natural persons".6
Walk through it in order, and write down the facts for each step:
- Is the intended purpose within Annex III point 4(a)? Use the provider's stated purpose and how Big Widget actually uses the tool.
- Does it profile natural persons? If yes, it is high-risk, and the derogation is closed. The Act's definition of profiling was not read for this module: not checked.
- If not, does it pose a significant risk of harm, including by materially influencing the outcome? A ranking that sets the order in which HR reads applications, or decides which ones HR reads at all, may shape the outcome. That is a fact to examine, not to assume.
- The rest of Article 6(3), and Article 6(4), were not read for this module. Any further conditions or procedure are not checked. Counsel owns this step.
Record the classification as a documented question with the facts relied on, not as a conclusion the scenario supplies. Whether the amending regulation changed Article 6's wording is not checked in this module.
Step 3: which date, from which text
The original Regulation (EU) 2024/1689 set its own timeline in Article 113: it applies generally from 2 August 2026, with Chapters I and II from 2 February 2025 and other parts on other dates.6 That 2024 timeline is not the end of the story. Regulation (EU) 2026/1744, adopted on 8 July 2026 and in force from the third day after its publication in the Official Journal, amends Article 113.7 Its Article 1(40)(b) provides that Chapter III, Sections 1 to 3, except Article 6(5), apply from 2 December 2027 for systems classified as high-risk under Article 6(2) and Annex III, and from 2 August 2028 for systems under Article 6(1) and Annex I.7 Its Article 1(40)(a) sets 2 December 2026 for listed Article 5 exceptions, and Article 1(40)(c) sets 27 July 2026 for Articles 102 to 110.7
Three cautions follow.
- This is not a blanket deferral. The amendment moves specific provisions. It does not defer the whole Act, and a duty dated in the future is not yet applicable.7
- Guidance is not the authority. The European Commission's AI Act page is a useful overview, but it is not the operative legal text.8 Cite the regulation and its amendment, version by version.
- Only parts of the amendment were opened for this module. These are Article 1(40), Article 4, the amended Article 111(2) below and recital 39. Whether other provisions of 2026/1744 change the wording of the articles in the table is not checked. Check a consolidated text before relying on any quoted wording.
Step 4: was the system already on the market or in service?
A start date says when a duty could first apply. It does not say the duty will reach this tool. Article 111(2), as amended by Regulation (EU) 2026/1744, says the Regulation applies to operators of high-risk AI systems "that have been placed on the market or put into service before the date of application of Chapter III referred to in Article 113, only if, as from that date, those systems are subject to significant changes in their designs".7 It opens "Without prejudice to the application of Article 5", and it sets a separate deadline of 2 August 2030 for providers and deployers of high-risk systems "intended to be used by public authorities".7 That carve-out turns on the system's intended use, not on who the operator is. Nothing in the stated facts says the hiring assistant is intended for use by public authorities; the transition memo records that as a fact to confirm.
So the 2 December 2027 dates in the table are the earliest dates those duties could apply. They are not a promise that they will. The role memo needs two more facts:
- When was the first unit of this assistant's type and model placed on the market or put into service in the EU? Before or after the Chapter III date? Recital 39 of 2026/1744 says that for this grace period "the decisive factor is the date on which the first unit of that type and model of high-risk AI system was placed on the market or put into service on the Union market for the first time".7 So Big Widget's own go-live date is not the answer. The memo records the provider's evidence for that first date and whether Big Widget's unit is the same type and model. The same recital extends the grace period where a unit "has been lawfully placed on the market or put into service" before the date.7 That lawful unit need not be the first one. So the memo keeps two separate facts: the first unit's date, and the provider's evidence that at least one unit of the same type and model was lawfully placed on the market or put into service before the Chapter III date. Chronology alone does not show the second. If any of these is unclear, or lawfulness is disputed, legal counsel rules, including on how the recital applies.
- On or after that date, does any change count as a significant change in its design? Who decides, and on what evidence?
How Article 111(2) works with the deployer duties below, and with Article 86, is a legal question. This module does not resolve it. Legal counsel rules on it, in writing, before the "start ranking" gate opens. Until then the gate answer is "wait for a person".
Step 5: the clause → gate → evidence → owner table
Scenario date: 18 November 2026. "Applies from" is the earliest date, read from the original Article 113 as amended by Article 1(40) of 2026/1744, for an Annex III system, if the system is classified high-risk, and subject to the transition row.
| Clause (original text) | Applies from (scenario reading) | Gate | Evidence | Owner | Open uncertainty |
|---|---|---|---|---|---|
| Art. 3(3), 3(4) definitions; Art. 25(1)(a)-(c) role shift6 | Art. 3 is in Chapter I: 2 Feb 2025 under original Art. 113,6 a date not among the Art. 1(40) changes recorded for this module.7 Art. 25 is in Chapter III Section 3: 2 Dec 2027 for Annex III systems under amended Art. 113.7 | Before configuration and before ranking use | Role memo: stated facts; the four missing role facts; contract, market and branding evidence | HR governance lead, with legal counsel | Provider capacity unresolved until development, placing-on-market, branding and modification facts are known |
| Art. 111(2) as amended: systems already placed on the market or put into service7 | Turns on the Chapter III date and on design changes on or after it7 | Before ranking use, and again at every design change | Transition memo: first EU market or service date for this type and model, and, as a separate fact, the provider's evidence that at least one unit was lawfully placed on the market or put into service before the Chapter III date, design changes made on or after the Chapter III date | Legal counsel, with the HR governance lead | Whether Chapter III duties reach this system at all; interaction with Art. 86 not checked |
| Art. 6(2), 6(3); Annex III point 4(a)6 | Art. 6(2) classification read with amended Art. 1137 | Before ranking use | Classification memo: intended purpose, profiling analysis, material-influence analysis | HR governance lead, with legal counsel | Classification not concluded; rest of Art. 6(3) and the amendment's effect on Art. 6 not checked |
| Art. 26(2): assign human oversight to people with the necessary competence, training and authority6 | 2 Dec 2027 (Chapter III Section 3)7 | Before ranking use | Named overseers, training record, authority to override | HR governance lead | Not yet applicable on the scenario date; adopted now as policy, not as a legal duty |
| Art. 26(6): keep the logs "automatically generated by that high-risk AI system to the extent such logs are under their control", for a period appropriate to the intended purpose, "of at least six months, unless provided otherwise in applicable Union or national law, in particular in Union law on the protection of personal data"6 | 2 Dec 20277 | Before ranking use | Log retention setting, owner, and the data-protection review of it | HR governance lead with IT and the privacy owner | Covers only automatic logs under Big Widget's control; depends on Art. 12 logging capability supplied by the provider |
| Art. 26(7): inform workers' representatives and affected workers before using the system at the workplace6 | 2 Dec 20277 | Before ranking use | Notice record | HR governance lead | Applies to workers; applicants are a separate question |
| Art. 26(11): inform people subject to Annex III decisions that the system is used6 | 2 Dec 20277 | Before ranking use | Applicant notice text and version | HR governance lead | Not yet applicable; adopted now as policy |
| Art. 12(1) logging; Art. 14(1) designed for effective human oversight (provider-side requirements)6 | 2 Dec 2027 (Chapter III Section 2)7 | Before ranking use | Provider's instructions for use; confirmation that logs and override exist | Provider; Big Widget too if it is a provider under Art. 25 | Who must meet these depends on Step 1 |
| Art. 86(1)-(3): an affected person subject to a decision taken by the deployer on the basis of output from an Annex III high-risk system, which produces legal effects or similarly significantly affects them in a way they consider adverse to their health, safety or fundamental rights, may obtain "clear and meaningful explanations of the role of the AI system in the decision-making procedure and the main elements of the decision taken". Para. 2 excludes uses where Union or national law provides exceptions or restrictions; para. 3 applies the Article only so far as Union law does not otherwise provide the right6 | Chapter IX, outside Chapter III Sections 1-3: the general date in original Art. 113 is 2 Aug 20266 | Before rejection | Decision record able to produce the explanation | HR governance lead | Not every rejection is in scope. Whether the right reaches this tool before the Chapter III duties apply, its interaction with Art. 111(2), and any amendment to Art. 86 are not checked; counsel rules |
| Big Widget policy (course design, not law): explain every rejection in plain words on request | Now, by company decision | Before rejection | Explanation sent, and its version | HR governance lead | A company promise, wider than the legal right; keep the two apart in every notice |
| NIST AI RMF GOVERN 2.1, MANAGE 4.11 | Voluntary: no application date | Supports the gates above | Mapping of each gate to the outcome it serves | HR governance lead | Guidance, not a legal duty1 |
| ISO/IEC 42001:20239 | Not a legal date | None claimed | None claimed | Not assigned | Clauses not checked; see below |
The rows that answer procurement are the first two. They test the deployer label against Articles 3 and 25, name the facts that could add provider capacity, ask whether the duties reach this system at all, and cite each clause and date from the legal text, not from guidance.
Where ISO/IEC 42001 fits
ISO's catalogue page identifies ISO/IEC 42001:2023 as edition 1, published December 2023, setting requirements for establishing, implementing, maintaining and continually improving an AI management system.9 This module has read the catalogue page, not the paid standard. So the table cites no ISO clause, and makes no claim about certification or about what certification would show. An ISO catalogue entry presented as a verified clause, or as proof of certification, is an error to reject.
Unknowns, with owners
The Foundation's Practice site says that "I don't know yet" "is always an answer, and it always pairs you with someone."5 In this table, that means every open item has a named owner. Legal counsel owns the transition question, Article 86's reach, the rest of Article 6(3) and any amendment not opened here. The HR governance lead owns the facts: who built the tool, when it went into service, whose name is on it and what changed. An open item is not a yes.
Why contestability and the audit trail come first
The misconception
A common belief is that an audit after deployment is enough to catch harm. Two public-sector failures, documented by the bodies that investigated them, show why that is not enough. Neither was a generative AI system, and neither is offered here as proof that one design choice would have changed what happened.
The Robodebt Royal Commission (Australia, 2023)
The Royal Commission into the Robodebt Scheme presented its report on 7 July 2023, and it was tabled that day; an updated edition followed on 11 July 2023 after corrections.10 This module uses only the recommendations reproduced on the report page.
- Recommendation 17.1 calls for a clear review path for people affected by automated decisions, plain-language information about automated decisions, and access to business rules and algorithms so that independent experts can scrutinise them.10
- Recommendation 17.2 says the Commonwealth should consider a body to monitor and audit automated decision-making for its technical aspects, fairness, bias and usability.10
These are recommendations: what should exist from now on. They are not, on their own, findings that each thing was missing in the Robodebt scheme, and this module does not use them that way. The report's chapters and the recommendations' implementation are not checked.
Read them as design requirements, and notice how much each asks. A review path, plain-language information and inspectable rules all have to exist before a decision is made, or the affected person has nothing to use. An auditing body needs records to audit.
Some easy answers are only partial. Telling applicants that a tool is used is a start on plain-language information; it does not explain how decisions are made. A log of setting changes is useful, but it may not show the rules the tool actually applies. Neither one gives an independent expert the business rules and algorithms. So Big Widget's regime adds three things:
- A rules pack. The configuration, thresholds, ranking criteria and provider documentation that actually drive a ranking, kept as a numbered version.
- A route for independent review. A named reviewer from outside the HR team can inspect the rules pack, under written access terms.
- A link from each decision to its rules and input. The decision record names the rules-pack version and where the application is kept, so the input can be recovered within the retention period.
If the provider will not let anyone outside see how the ranking works, write that down as a gap, with an owner. Do not call a change log "access to the rules".
Ongekend onrecht (the Netherlands, 2020)
The Dutch parliamentary inquiry into the childcare benefit reported on 17 December 2020 under the title Ongekend onrecht ("unprecedented injustice").11 It states: "De commissie constateert dat bij de uitvoering van de kinderopvangtoeslag grondbeginselen van de rechtsstaat zijn geschonden."11 In this course's translation: the committee finds that fundamental principles of the rule of law were violated in administering the childcare benefit. The report also describes repeated late, incomplete and incorrect information to Parliament, and deficient information management within ministries.11
Two limits. The report explicitly leaves nationality-based risk profiles outside its remit and refers to the data-protection authority's separate investigation, so findings of that investigation are not attributed to this report.11 And this is a governance and redress case, not proof that a single model caused the scandal.11
What the two cases teach the designer
| What the source records (recommendation or finding) | Design requirement it supports | Where it sits in Big Widget's regime |
|---|---|---|
| Recommended: a clear review path (Rec. 17.1)10 | A challenge route that exists before the first decision, with a reviewer who can reverse | "Reject" and "resolve a challenge" rows |
| Recommended: plain-language information about automated decisions (Rec. 17.1)10 | Notice in advance, in plain words. Partial on its own: it says the tool is used, not how it decides | Applicant notice at go-live; explanation on request |
| Recommended: access to business rules and algorithms for independent scrutiny (Rec. 17.1)10 | The operative rules, versioned, open to an independent expert under stated terms. A change log alone falls short | Rules pack; independent review route; change log; role and classification memos |
| Recommended for consideration: a body to monitor and audit automated decisions (Rec. 17.2)10 | Records kept from the start, so there is something to audit | Decision and challenge records |
| Found: late, incomplete and incorrect information; deficient information management (p. 8)11 | An end-to-end trail that links each outcome to its inputs, rule version and decider | Decision record; Raji and colleagues' stage documents3 |
Missing records and missing remedy powers limit what a later audit can reliably rebuild or put right. Other records or testimony may fill some gaps, and a remedy created later may help some people. But a regime cannot promise either to the people it has already decided about. That is why Raji and colleagues place audit documents at each stage of development, not at the end,3 and why NIST lists appeal and override among the mechanisms a post-deployment plan should include.1
The quiz asks you to match a proposed challenge route to the barrier it addresses. It does not ask whether the route would have changed what happened in Australia or the Netherlands; the sources do not answer that, and neither does this module.
Regime check
- Decider, gate, evidence, remedy. These four are this course's test. NIST asks for some of the same things, such as documented roles and mechanisms for appeal and override.1 If any column is blank for a consequential action, the regime is incomplete, whatever framework it cites. A stop gate may be "always allowed", if the regime says so in writing.
- Validate the role; date the duty; check the transition. Test "deployer" against Articles 3 and 25 and list the missing facts.6 Read each duty's date from the original text as amended, not from the 2024 timeline alone or from guidance.7 8 Then ask when the system was placed on the market or put into service, and what has changed in its design since.7
- Keep guidance and catalogues in their place. NIST is voluntary;1 the ISO entry here is a catalogue page with no checked clause.9
- Design the challenge in. A review path and an audit trail must exist before the first decision.10 11 A notice and a change log are partial answers; independent scrutiny needs the operative rules.
- Keep receipts clean. A signed receipt carries metadata only, never personal data.5 The applicant's details stay in the controlled decision record.
Words to know: governance regime, decider, gate, evidence, remedy, provider, deployer, placing on the market, substantial modification, intended purpose, profiling, application date, transition, significant change in design, rules pack, contestability, audit trail, receipt.
Further learning (not cited, never copied): Stanford CS 181 (Computers, Ethics, and Public Policy), Harvard CS 2881R (AI Safety) and Cambridge's Practical Research in Human-centred AI, listed in this module's source pack and in levels/500/universities.md.